
reCAPTCHA v2 vs. v3: An Outdated Approach to Bot Protection
The promise of Google’s reCAPTCHA v3 is to prevent bot traffic to your website without the user friction we all associate with v2. But does reCAPTCHA v3 keep its promise?
Let’s take an honest look at what reCAPTCHA v3 can and cannot do for your website security. We’ll detail the differences between reCAPTCHA v2 vs. v3, uncover the pitfalls of reCAPTCHA v3 configuration, and sum up what truly effective bot protection and mitigation software must deliver.
What is reCAPTCHA?
First things first: A CAPTCHA (acronym for “Completely Automated Public Turing Test to Tell Computers and Humans Apart”) is a security measure designed to differentiate bots from humans, typically with an image or audio challenge. CAPTCHA was a Carnegie Mellon research project first launched in 2000 as a general-purpose authentication technique for humans.
Intended for very low-level validation, CAPTCHAs have not historically been coupled with security logic. But today, CAPTCHAs are widely used on the internet to prevent bots from signing up for accounts, spamming comments, and buying products. Unfortunately, they are no longer effective against modern, sophisticated bots.
ReCAPTCHA is what Google calls its CAPTCHA system. It was released in 2007 and is currently used by more than 13 million live websites. Despite some controversy around its privacy compliance with GDPR and similar policies, reCAPTCHA has been the most-used CAPTCHA system to date.
Is reCAPTCHA free?
reCAPTCHA is free only up to a point. Google now manages reCAPTCHA through Google Cloud, and the free tier covers just 10,000 assessments a month. That quota is shared across your entire Google Cloud organization, not each site. To go past it, you must enable billing.
Beyond the free tier, Google charges a flat $8 a month for 10,001 to 100,000 assessments, then $1 for every 1,000 above that. So if your website generates three million assessments a month, your reCAPTCHA bill will be roughly $3,000 every month.
reCAPTCHA v2: Hard on humans, too easy on bots
Many websites are still using reCAPTCHA v2, which was launched in 2014. If a user’s behavior triggers suspicion, reCAPTCHA v2 will provide a challenge that the visitor must solve to prove they’re human.
We’re all familiar with the various versions of reCAPTCHA v2. Sometimes, all you need to do is check a box that says “I’m not a robot.” Other times, reCAPTCHA will challenge you with an image or audio recognition task. Whether or not you get the full challenge will depend on how confident Google is that you really are a human.

reCAPTCHA v2 is based on an “advanced risk analysis system” that relies quite heavily on Google cookies. If someone is browsing the web using Chrome, or has been logged into a Google account for a while, they’ll most likely just have to tick a box. On the other hand, a Firefox user who has disabled third-party cookies is much more likely to get a difficult image recognition challenge.
Not everyone uses Chrome, and not everyone is comfortable using Google’s services due to online privacy concerns. Still, the privacy-conscious might use browsers like Firefox or Brave, or even a VPN to browse the internet—only to face tougher challenges from reCAPTCHA v2, which degrades their user experience and lowers conversion rates.
Additionally, due to the ubiquity of reCAPTCHA v2, cybercriminals have found increasingly efficient automated solutions to bypass even the most difficult reCAPTCHA v2 challenges, especially with advancements in AI models.
CAPTCHA farms
Cybercriminals can also outsource reCAPTCHA challenges by sending them to human workers at CAPTCHA farms in low-cost countries. Thanks to CAPTCHA farms, attackers can use bots that don’t need to execute JavaScript. To pass a reCAPTCHA v2, all a bot has to do is send a callback request containing the response token provided by the CAPTCHA farm.
Without the need for JavaScript, attackers can create bots that leverage simple HTTP request libraries instead of having to use fully automated browsers like Selenium or Puppeteer with headless Chrome. This decreases their infrastructure cost, so they can crawl pages faster or stuff more credentials. The fees they pay the CAPTCHA farms are minor in comparison: it costs approximately $1-3 to solve 1,000 v2 reCAPTCHAs.
reCAPTCHA v3: Easy on humans, except website admins
After listening to some of the user complaints, Google developed reCAPTCHA v3 to provide a better user experience. Unlike v2, reCAPTCHA v3 is invisible for website visitors. There are no challenges to solve. Instead, reCAPTCHA v3 continuously monitors each visitor’s behavior to determine whether it’s a human or a bot.
Currently, reCAPTCHA v3 is in use on just over 1.2 million live websites, versus the 10 million+ sites using v2.
How does Google reCAPTCHA v3 work?
For each request the user makes, reCAPTCHA v3 returns a score between 0 and 1 to represent the likelihood that the request originated from a bot. If the score is close to 0, it’s likely a bot—and if it’s close to 1, it’s more likely to be a human. As in v2, users who are logged into their Google accounts and/or using Chrome are more likely to have a score close to 1.
To improve the accuracy of the score, website administrators can define specific actions, such as “sending a friend request” or “go to homepage” to help the reCAPTCHA understand how normal user behavior will vary depending on the context. While reCAPTCHA v3 clearly improves the experience for human users by eliminating the need to disrupt their browsing with reCAPTCHA challenges, it still raises privacy concerns and creates problems for website administrators.
With reCAPTCHA v2, administrators only need to verify whether the user correctly solved the challenge or not. With reCAPTCHA v3, administrators need to decide which action to take depending on the users’ score. Getting this configuration right is a tricky task for even the most experienced webmaster.
Mapping reCAPTCHA v3 user scores to actions
For each action a user takes on your website, you have three possible responses:
- Give the user access to the requested resource.
- Ask the user to solve a reCAPTCHA to determine if they’re human.
- Block the user (hard block).
This means that you need to decide for each action where you want to place the threshold for a particular response. Will you block the user when their score falls below 0.25, or will you serve them a reCAPTCHA? What about 0.15? Will you fully block them then, or does 0.10 seem more appropriate? What happens if a user fails a reCAPTCHA challenge? There are no clear-cut answers, which is what makes these questions so difficult.
The stricter you make your thresholds, the more likely you are to block actual users. The contrary is also true: the looser your thresholds, the more likely you are to leave bots undetected. With reCAPTCHA v3, you need to make an unpleasant compromise between not blocking too many users and not allowing too many bots.
No feedback loop
The reCAPTCHA v3 dashboard displays a distribution of user scores for each configured action on your website. But that’s not enough to help you assess whether you’ve set the right thresholds, because there’s no other information to help you better understand the users you’ve blocked or let through. There is no way to look into possible false positives or negatives.
It’s important to consider that the Internet is far more diverse than we often imagine it to be. Sure, the majority of your legitimate users might browse the internet with Chrome, Edge, or Safari, but what about the ~8% of people who don’t? Their user scores will be significantly lower. Do you really want to make their lives harder with a reCAPTCHA or by blocking them outright?
Setting blocking and authorization thresholds without a proper monitoring mechanism is like playing Russian roulette with your website’s traffic. Collecting, storing, and analyzing enough data to set your thresholds accurately requires deep bot detection knowledge and significant software development costs.
Detection quality
ReCAPTCHA v3 uses behavioral detection to predict whether a given request originates from a human or not. While behavioral detection is extremely helpful for detecting advanced bots, learning how to distinguish bots from humans accurately requires huge volumes of data.
To make an accurate decision, reCAPTCHA v3 needs data—it needs a user to interact with your website for a while. With reCAPTCHA alone, your site is vulnerable to large-scale distributed crawlers that rotate through several IP addresses.
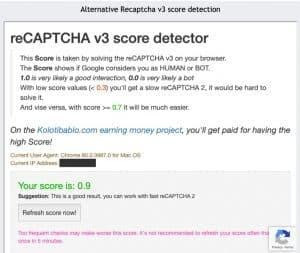
Here at DataDome, we did a quick experiment to determine whether reCAPTCHA v3 also uses basic client-side fingerprinting signals—and it does. While v3 can easily detect “naive” bots, such as those that use unpatched Selenium bots or don’t remove the navigator.webdriver attribute, bots that forge their fingerprint easily bypass reCAPTCHA v3 detection.
We created a Headless Chrome bot and used the Puppeteer extra framework to forge its fingerprint, then had it screenshot its reCAPTCHA v3 score. It had obtained a nearly “human” user score of 0.9: a perfect intruder.
reCAPTCHA & privacy compliance
Countries around the world have begun to implement privacy-focused regulations, such as the General Data Protection Regulation (GDPR) in the European Union. Online tools like reCAPTCHA should be compliant with these regulations.
However, in July 2020, France’s Commission Nationale Informatique & Libertés (CNIL) found that Google’s reCAPTCHA was not privacy-compliant. Because reCAPTCHA can gather user data that is transmitted to Google for “analysis”, GDPR says end-users of platforms that use reCAPTCHA must be informed that their data is being collected, and they must have an option to consent or opt out of sharing their data.
Google leaves it up to the companies that use reCAPTCHA to inform and get consent from their end-users, which often does not happen, as the CNIL discovered. And since the purposes of reCAPTCHA’s data collection are not precisely defined, it is difficult to imagine how user consent—even if collected—could meet the GDPR requirements of being “free, specific, informed, and unambiguous.”
Just as businesses need to trust that real humans are interacting with their platforms, their customers and end-users need to trust that their data won’t be compromised.
Make sure you can trust any solution or provider that can impact your customer relationships (including your bot and online fraud management and your CAPTCHA provider) to prioritize your end-users’ privacy as much as you do.
Can bots bypass reCAPTCHA?
In short, yes they can. While reCAPTCHA v2 and v3 can help limit simple bot traffic, both versions come with several problems:
- User experience suffers, as human users hate the image/audio recognition challenges.
- CAPTCHA farms and advances in AI allow cybercriminals and advanced bots to bypass reCAPTCHAs easily.
- Defining the right thresholds for reCAPTCHA v3 user scores is a very difficult task.
There’s no way to monitor false positives and negatives. The bottom line is that neither reCAPTCHA v2 nor v3 are replacements for a proper bot management solution.
The modern alternative to reCAPTCHA: Invisible verification first
DataDome’s CAPTCHA alternative is a secure, user-friendly, and privacy-compliant replacement for puzzle-based verification with two layers:
- Device Check is the invisible first layer. It analyzes dozens of device, browser, and network signals in milliseconds, with no user interaction.
- Slider is the step-up layer, shown only when our detection engine needs more signals. It collects behavioral data, like mouse movements and touch dynamics, in a median of one second.
Both are WCAG 2.2 compliant and available in 50+ languages. And because we analyze the behavior behind a solved Slider rather than treating it as proof of humanity, AI solvers and CAPTCHA farms don’t get through.
No thresholds to tune
Unlike reCAPTCHA v3, there are no scores to map to actions. Install our server-side module and mobile SDK, allowlist your partners’ bots, and you don’t need to add any other detection logic or thresholds. DataDome also recognizes good bots, like search engine bots and SEO crawlers, so you don’t risk accidentally hurting your SEO rankings.
Want more control? Add custom rules, or enable and disable Device Check and the Slider per endpoint.
A feedback loop reCAPTCHA doesn’t have
DataDome’s false-positive rate is less than 0.01%. In the rare case a human sees a challenge, our real-time feedback loop passes that information to our detection engine in under 2 milliseconds. Our bot SOC analysts also review traffic regularly, and our dashboard lets you explore bad bot activity and verifications served by IP address, country, type of bot blocked, and more.
Detecting what reCAPTCHA v3 misses
We analyze each request individually in under 2 milliseconds. A bot that received a 0.9 score from reCAPTCHA v3 would be detected by DataDome, including advanced bots that use residential IP proxies, forged fingerprints, or headless browsers automated with modified Puppeteer, Playwright, or Selenium. We detect them at the first request.
In Conclusion
reCAPTCHA v2 and v3 can filter simple bots, but both can degrade the user experience, be bypassed by CAPTCHA farms and advanced bots, raise GDPR concerns, and provide no real feedback mechanism. Neither replaces a real bot management solution.
DataDome’s CAPTCHA alternative solution, with Device Check first and the Slider only when needed, stops advanced bots without making your customers prove they’re human. Book a demo today to see it in action.
FAQs
reCAPTCHA v2 shows visitors an “I’m not a robot” checkbox and, if the visit looks suspicious, an image or audio challenge. reCAPTCHA v3 is invisible: it runs in the background and returns a score from 0 to 1 for each request, where a score closer to 1 means the visitor is more likely human. With v3, you decide what to do at each score: allow, challenge, or block.
For visitors, yes: v3 removes the challenges. For website admins, it’s harder. You have to set score thresholds for each action, and the dashboard gives you no way to check for false positives or negatives. Neither version is a full bot protection solution: v2 can be outsourced to CAPTCHA farms, and in our test, a bot with a forged fingerprint received a 0.9 “human” score from v3.
It can stop simple bots, such as unpatched Selenium bots. But CAPTCHA farms, AI solvers, and bots with forged fingerprints can bypass it, and it adds friction for real users. For protection against scalping, scraping, and account takeover, you need a bot protection solution like DataDome.
It’s bypassed more than hacked. For v2, attackers send challenges to human workers at CAPTCHA farms or use AI solvers. Bots then submit the response token without running JavaScript, at roughly $1-3 per 1,000 solves. For v3, bots that forge their browser fingerprint can earn a high human score.
Use a bot protection solution that verifies visitors without relying on puzzles. DataDome’s CAPTCHA alternative starts with Device Check, an invisible verification layer, and shows the Slider only when more signals are needed. It protects websites, mobile apps, and APIs against threats like account takeovers, credential stuffing, and web scraping.
It depends on your priorities. hCaptcha positions itself as a privacy-focused alternative to Google’s reCAPTCHA, which drew a GDPR ruling from France’s CNIL in 2020. But both rely on visitors solving a challenge, and any challenge-based first line of defense can be outsourced to CAPTCHA farms or AI solvers.

Related posts
How SMG Blocks Millions of Scrapers Daily to Protect Switzerland's Leading Marketplace Platforms
Tell me more
How 1001Pneus Blocked Competitor Price Scrapers & Reclaimed Its Competitive Edge
Tell me more
How to Stop Bot Traffic From Crashing Your Site During Black Friday 2026
Tell me more
Which Industries Are Least Protected From Bots & Spoofed AI Agents in 2026?
Tell me more