


What Is a CAPTCHA? Definition, Types & How It Works
You’ve almost certainly run into a CAPTCHA online. There’s a reason they keep showing up: bots now make up a growing percentage of online traffic, and bad bots are built to hit your forms, break into accounts, and harvest your data.
CAPTCHAs were designed to stop them. But in the age of AI, a CAPTCHA on its own is no longer enough.
What is a CAPTCHA?
CAPTCHA stands for “Completely Automated Public Turing test to tell Computers and Humans Apart.” It’s a challenge-response test that websites use to tell real users from bots.
The first CAPTCHAs appeared in the late ’90s: distorted letters and numbers that people could read and machines couldn’t.
How do CAPTCHAs work?
When a CAPTCHA is triggered, a challenge appears as users try to reach a page or submit information. Early text CAPTCHAs twisted and warped characters, then added color gradients and background noise to confuse bots. Later versions asked users to pick out images containing a given object. Some versions, like invisible reCAPTCHA, run in the background.
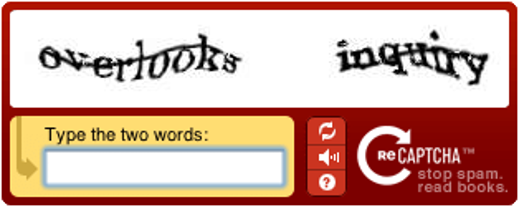
An example of an early CAPTCHA
The logic is simple: if the challenge isn’t triggered, or is passed, the visitor is treated as human. If it’s failed, the visitor is treated as a bot. Most CAPTCHA systems can’t detect their own false positives or false negatives. And all types of traditional CAPTCHA, reCAPTCHA included, have been outpaced by bot developers.
What triggers a CAPTCHA test?
Ideally, suspicious behavior. Common triggers include:
- IP tracking: The visitor’s IP has been flagged as a bot.
- Resource loading: The visitor doesn’t load styles, banners, or images.
- Sign-in state: The visitor isn’t signed in to Google when accessing the site.
- No browsing history: Real humans do more than hit the same login page over and over.
- Traffic volume: Requests arrive too quickly from a single source.
- User agent anomalies: Browser identification strings are unusual or missing.
- Bot-like behavior: Odd click patterns, little mouse movement, and perfectly centered checkbox clicks.
What is the difference between CAPTCHA and reCAPTCHA?
CAPTCHA is the generic term for any challenge-response test that separates humans from bots. reCAPTCHA is Google’s specific implementation. Here are the main differences:
- Technology: reCAPTCHA adds IP tracking, behavioral analysis, and machine learning. Traditional CAPTCHAs rely mostly on visual or audio challenges.
- User experience: reCAPTCHA offers lighter interactions (a checkbox, mouse tracking) over squinting at warped text.
- Data collection: reCAPTCHA analyzes extensive user behavior. Basic CAPTCHAs only evaluate the answer given.
- Evolution: reCAPTCHA has gone through v1, v2, and v3. Traditional CAPTCHAs have barely changed.
Want the full breakdown? See our CAPTCHA vs. reCAPTCHA comparison.
What are the different types of CAPTCHA?
Text CAPTCHA
For years, the most common type. Users type a distorted, blurred, or obscured word to pass. Techniques include Gimpy (several dictionary words), EZ-Gimpy (one word), Gimpy-r (random letters with noise), and Simard’s HIP (random letters and numbers distorted with arcs and colors).
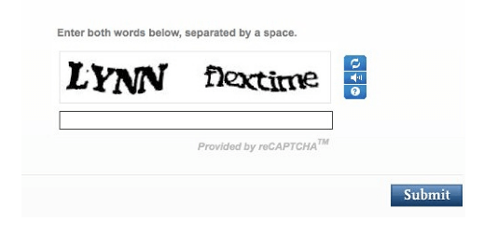
Text CAPTCHAs are hard to read and hard to access, especially for people with visual impairments.
Image CAPTCHA
Users pick the images that contain a specified object. Image recognition is easy for humans, and until recently was hard for machines. Google, for example, pairs its Street View library with AI to generate challenges on the fly. (That’s why you keep clicking on street signs and fire hydrants.) Variations include picking objects from a collage, rearranging jigsaw-like pieces, rotating images upright, and finding objects in complex scenes.

Audio CAPTCHA
An accessibility fallback: users click a speaker or headphones button and type the numbers or letters they hear.
Risk-scoring CAPTCHA
No puzzle at all. reCAPTCHA v3 monitors on-page behavior and assigns each visitor a score from 0.0 (likely a bot) to 1.0 (likely human). The site decides what to do with that score.
Press-and-hold CAPTCHA
Users press and hold a button while the system analyzes how they interact. It’s a lighter, behavior-based variant now common on retail sites.
Other CAPTCHA formats
Some sites move away from traditional CAPTCHAs toward other types:
- Math problem: Solve something basic, like 3+2.
- Word problem: Rearrange letters, name the color of the text, or give the last word of a sentence.
- Social media sign-in: Log in with a Google or Facebook account.
- Time-based: Visitors who complete a form in a fraction of a second are blocked.
- No CAPTCHA reCAPTCHA: Tick “I’m not a robot” while Google tracks mouse movement and other signals.
- reCAPTCHA v3: Invisible scoring, no user interaction.
What are CAPTCHAs used for?
CAPTCHAs aim to keep bots posing as humans away from resources meant for people. Bad bots can:
- Create fake accounts to waste resources, overload servers, spam users, and launch phishing campaigns. Learn how to stop fake account creation.
- Take over sites by flooding comments and contact forms with dangerous links.
- Enable scalpers to buy up in-demand tickets and products, then resell them at a markup.
- Skew polls and ratings by voting at scale.
- Abuse payment flows by testing lists of stolen card data.
You’ll see CAPTCHAs most often at e-commerce checkout, account registration, contact forms, and polls or surveys.
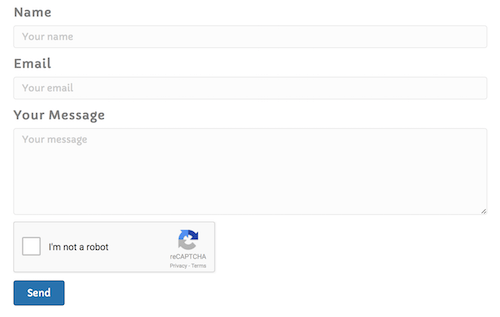
CAPTCHAs are common on contact forms
What are the cons of CAPTCHAs?
CAPTCHAs are not a reliable standalone defense against modern bots. They also come with real costs for the humans they’re meant to protect:
- Failed challenges: In a usability study of 1,027 participants, Baymard Institute found that 8.66% of users mistyped a text CAPTCHA on their first attempt. That jumped to 29.45% when the CAPTCHA was case-sensitive.
- User experience: A CAPTCHA interrupts what people are trying to do. Some abandon the page altogether.
- Accessibility: CAPTCHAs rely on visual perception, which makes them close to impossible for anyone with seriously impaired vision.
- Browser compatibility: Some types don’t support all browsers or older devices.
- Privacy: reCAPTCHA collects extensive user data for Google’s advertising ecosystem, raising GDPR and privacy compliance questions.
Why do CAPTCHAs fail against modern bots?
CAPTCHAs were built for a simpler threat. Three flaws explain why they now fall short:
- They test the puzzle, not the intent. A CAPTCHA only checks whether something can solve a challenge. Today, bots can.
- They’re a single signal. Pass or fail is all a siloed CAPTCHA knows. Sophisticated bots are caught by combining many signals, not one.
- They hurt the wrong side. Real users absorb the friction. Attackers just route around it.
The result: roughly half of CAPTCHA solves come from bots.
Dig deeper: How effective is CAPTCHA? Why it’s not enough for bot protection.
How do advanced bots bypass CAPTCHAs?
- Machine learning solvers: AI-powered bots now solve many text and image CAPTCHAs, and do it faster than humans.
- CAPTCHA farms: Attackers outsource challenges to low-paid human workers (or automated solvers) for pennies per solve. In one case, DataDome stopped a CAPTCHA farm that fired 18.8 million bypass attempts at a single ticketing platform in about 24 hours, from a botnet spanning 3.2 million IP addresses.
- Behavioral mimicking: Bots simulate human mouse movements, click patterns, and browsing to fool behavioral checks.
- Browser automation tools: Headless browsers and automation frameworks run JavaScript and mimic legitimate fingerprints.
What are the alternatives to CAPTCHA?
- Honeypots: Hidden form fields. People can’t see them. Bots fill them in and give themselves away.
- Two-factor authentication (2FA): Requires two forms of identification, such as a password plus a code sent to a phone.
- Behavioral analysis: Spots bots by how they navigate: speed, mouse and touchpad patterns, scrolling and tapping.
- Email verification: Confirms identity with a link or code sent to the user’s inbox.
- Proof-of-work challenges: The browser silently solves a cryptographic puzzle, which is cheap for one human visitor and costly for a bot sending thousands of requests.
- Advanced bot detection: Machine learning, device fingerprinting, and real-time behavioral analysis identify bots without asking users to do anything.
See our full guide to CAPTCHA alternatives.
DataDome: A frictionless CAPTCHA alternative
Traditional CAPTCHAs fail against modern bots and create a frustrating user experience. DataDome takes a verification-first approach instead.
DataDome analyzes over 5 trillion signals daily to detect the intent behind your traffic in real time—whether from a human, bot, or AI agent. With DataDome, most visitors never see a challenge. Only when extra verification is needed to users see DataDome’s CAPTCHA alternative: a quick, accessible, privacy-compliant check that gathers more behavioral data without a single puzzle.
With an industry-leading false positive rate of 0.01%, DataDome keeps legitimate users moving without friction. Book a demo to see the platform in action.
FAQs
No. Advanced bots and CAPTCHA farms can bypass most challenges, and roughly half of the traffic that solves a CAPTCHA is actually a bot, not a human. Effective protection layers passive, invisible detection (device fingerprinting, behavioral analysis, network signals) and treats a visible CAPTCHA as a last resort, not the primary control.
Most modern implementations don’t show a CAPTCHA to every visitor. They evaluate signals like IP reputation, request volume, browser and device consistency, and behavior first, and only trigger a visible challenge when they can’t confidently classify the visitor as human or bot.
CAPTCHA is the general category of human-verification tests. reCAPTCHA is Google’s specific implementation, which has evolved from distorted text to image grids, a one-click “I’m not a robot” checkbox, and an invisible, score-based version (reCAPTCHA v3) that rates risk from 0.0 to 1.0 without any interaction. Learn how reCAPTCHA works.
Not very. Baymard Institute found that 8.66% of users mistyped a text CAPTCHA on their first attempt, rising to 29.45% for case-sensitive challenges. Real visitors get blocked or frustrated while sophisticated bots increasingly pass.
Not on their own. CAPTCHA farms use low-cost human workers (or automated solvers) to solve challenges on demand, so bot operators can route any CAPTCHA to a real human and get a valid pass back in seconds. In one documented case, DataDome stopped a CAPTCHA farm that generated 18.8 million bypass attempts against a single ticketing platform in about 24 hours, from a botnet spanning 3.2 million IP addresses. Learn more about CAPTCHA bots.
Instead of showing every visitor a puzzle, modern bot management platforms evaluate device, network, and behavioral signals invisibly. They reserve a lightweight challenge, like DataDome’s CAPTCHA alternative, for the small share of traffic they can’t classify with confidence.

Related posts
Why Layering a Specialist Bot & Agent Trust Solution With Your CDN Is Now Essential
Tell me more
Introducing DataDome’s AI Key Takeaways Feature: Understand Your Protection at a Glance
Tell me more
Beyond Detection Accuracy: Measuring the Real Business Impact of Bot Management
Tell me more
How Kiabi Cut Malicious Login Attempts & Gained Instant Threat Visibility
Tell me more

